

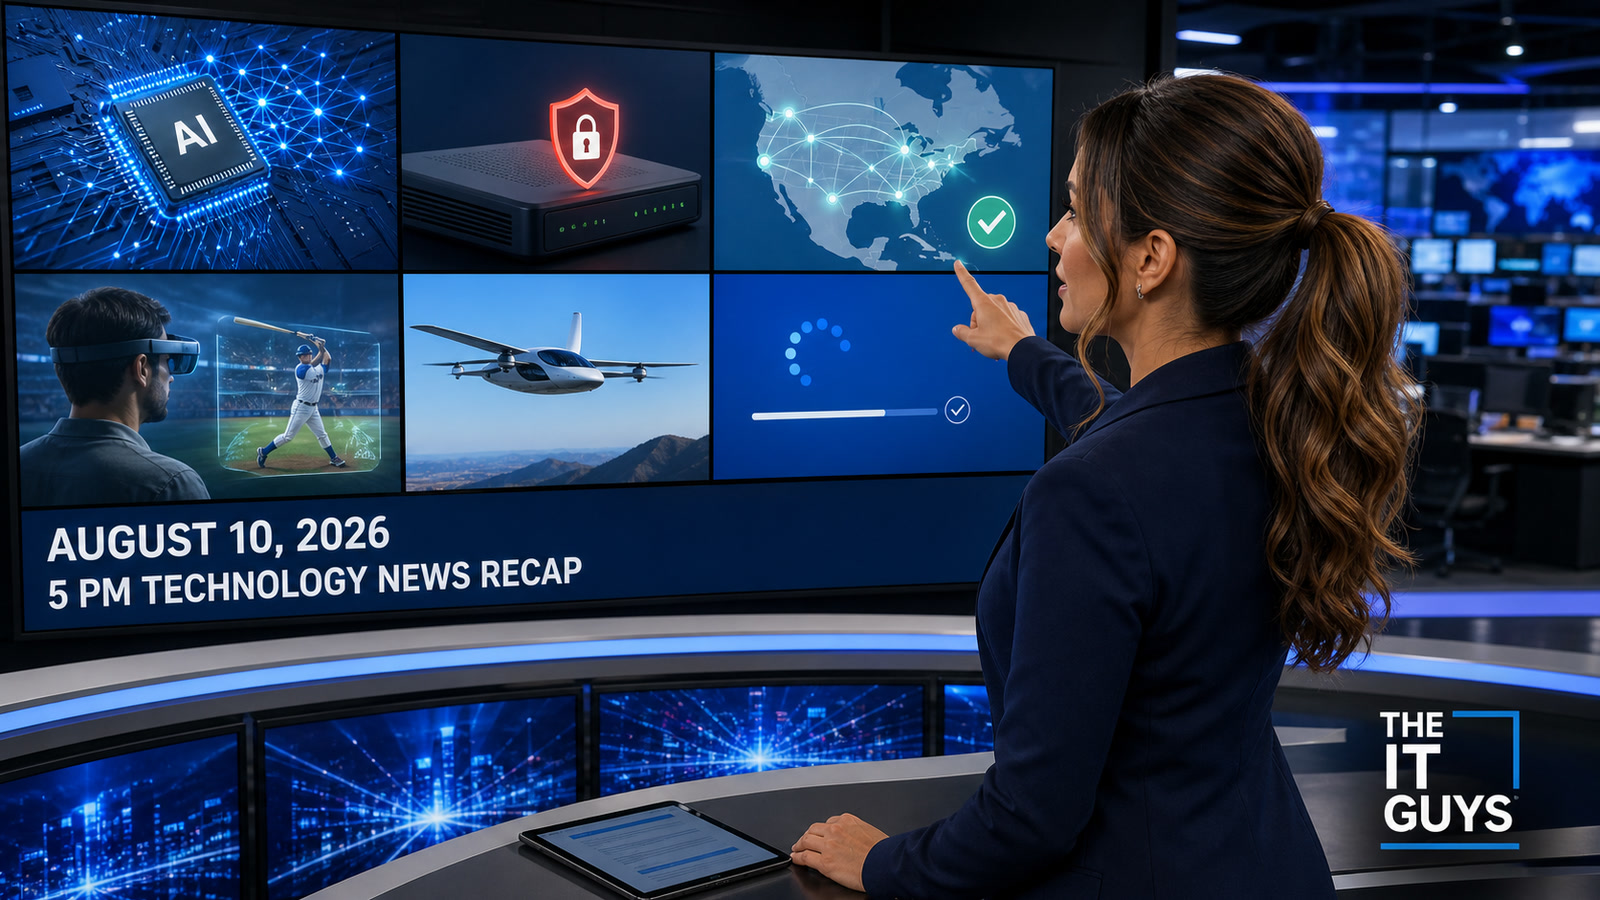
Tonight’s technology picture is split between useful local AI, urgent edge-system patching, a resolved regional DNS incident, and two ambitious bets on immersive media and autonomous aviation. The practical priority is clear: patch exposed infrastructure first, verify recovery before changing network settings, and treat shiny new AI or spatial-computing claims as things to test—not promises to accept on faith.
Listen to the 5 PM recap
Locally synthesized narration of this broadcast-ready edition. No OpenAI voice service was used.
Tonight’s rundown
- Meta releases MuseGlimmer: a 30-billion-parameter open-weight model designed for local agent work—but “consumer hardware” means a high-end machine.
- Security deadline: CISA’s federal remediation date arrives for an exploited Progress LoadMaster command-injection flaw.
- Build systems under attack: JetBrains says unpatched on-premises TeamCity servers face active exploitation.
- Cloudflare DNS recovers: a minor, regional 1.1.1.1 degradation in Tel Aviv was resolved; it was not a global outage.
- Apple’s immersive baseball test: the company schedules its first live Friday Night Baseball presentation in Apple Immersive for August 28.
- Autonomous aviation consolidation: Boeing agrees to transfer Wisk, SkyGrid, and Insitu to Archer in a stock transaction.
1. Meta’s MuseGlimmer puts a capable local agent model within reach—if your hardware is genuinely high-end
Meta released MuseGlimmer, a 30-billion-parameter model optimized for local agent workflows. Meta says the model accepts text and images, supports tool calling, coding, file-oriented work, and long-running task execution, and was trained with data from more than 100 languages. The weights are available under the permissive Apache 2.0 license.
The headline is “runs on your device,” but the memory math matters. Meta says full precision would require more than 55 GB. Its quantized language model is under 20 GB, with a named 17 GB quantized build intended to leave room for working memory and its image encoder inside a 24 GB or 32 GB memory envelope. That is plausible local-agent territory for premium workstations and certain high-memory Macs—not a promise that an ordinary family laptop will run it comfortably.
Local inference can reduce dependence on a cloud connection and may keep some prompts and files on the device. It does not automatically make an agent safe. A model with permission to read files, send messages, invoke scripts, or manage a calendar still needs least privilege, logs, confirmation boundaries, and a sandbox. Meta’s benchmark, speed, and “minimal degradation” statements are vendor-reported; independent testing should decide whether the model is useful for a specific workload.
2. Progress LoadMaster owners have no room left for “we’ll patch later”
CISA added CVE-2026-8037, a Progress LoadMaster OS-command-injection vulnerability, to its Known Exploited Vulnerabilities catalog on August 7 and set August 10 as the remediation due date for covered federal agencies. The Progress bulletin provides the vendor path.
The important phrase is unauthenticated command execution. CISA says unsanitized input in multiple command endpoints can allow an attacker to run arbitrary commands. Because LoadMaster sits at the edge of a network and routes application traffic, compromise can expose far more than one appliance. CISA confirms exploitation in the wild; its catalog lists known ransomware use as “Unknown,” which is not the same as “none.”
The federal deadline does not automatically become a legal deadline for every private company. It is still a strong operational urgency signal. Internet-facing load balancers should be inventoried, compared against Progress’s affected and fixed versions, and patched or mitigated immediately. If compromise is plausible, preserve logs before a reset or rebuild, review administrator changes and outbound connections, and scope downstream systems rather than treating an appliance reboot as incident closure.
3. JetBrains warns that unpatched TeamCity servers are being targeted
JetBrains says it received reports of active and attempted exploitation against unpatched on-premises TeamCity servers through CVE-2026-63077. According to its August 7 guidance, an attacker with HTTP or HTTPS access can exploit the agent-polling protocol without authentication and run commands with the privileges of the TeamCity server process.
A build server is a crown-jewel system: it can hold repository credentials, signing material, deployment tokens, configuration, build artifacts, and access to downstream environments. That means defenders should not stop after installing a patch. Fixed releases include 2025.11.7 and 2026.1.3; JetBrains also offers a security patch plugin for TeamCity 2017.1 and later. The plugin is a narrow mitigation for this CVE, not a replacement for moving to a current supported release.
TeamCity Cloud was already mitigated and requires no customer action. On-premises operators should review newly created accounts and tokens, unexpected child processes from the TeamCity service, build-configuration changes, credential access, and modified artifacts. If a server was exposed while vulnerable, rotate secrets only after containing the system so newly issued credentials are not immediately captured again.
4. Cloudflare’s Tel Aviv 1.1.1.1 issue was real, regional, and resolved
Cloudflare reported degraded recursive-DNS performance for some 1.1.1.1 users in Tel Aviv at 10:15 UTC. The company identified the problem, implemented a fix, monitored recovery, and marked the incident resolved at 12:19 UTC. Cloudflare classified the impact as minor.
This is a useful lesson in outage discipline. A regional resolver problem does not justify an organization-wide emergency DNS migration after the incident is over. Confirm whether affected users and geography match the status report; check multiple resolver paths; examine local firewall, DHCP, and upstream-provider health; and only then change configuration. Cloudflare did not publish a cause, affected-user count, or request volume, so it would be wrong to inflate this into a worldwide 1.1.1.1 failure.
If a local network still looks “totally down,” do not overlook a self-inflicted Layer 2 problem. The IT Guys’ new guide explains how to find an Ethernet loop or broadcast storm before resetting the router. For resilience planning rather than emergency improvisation, use our backup-internet failover checklist.
5. Apple schedules its first live immersive baseball broadcast for August 28
Apple and Major League Baseball announced that the August 28 Red Sox–Yankees game will be the first live Friday Night Baseball presentation in Apple Immersive. Apple’s announcement promises 8K stereoscopic video, a 180-degree field of view, Spatial Audio, dedicated replays, and immersive graphics for supported Vision Pro owners with an Apple TV subscription in named regions including the United States.
This is a technically meaningful test because live sports combine fast motion, camera switching, low-latency delivery, graphics, audio synchronization, and sustained headset comfort. It is also only an announcement. Until the game happens, nobody outside the production pipeline can verify final image quality, motion handling, latency, or comfort over an entire broadcast.
Vision Pro owners who already have the equipment can update their software, confirm regional and subscription eligibility, and put the game on the calendar. Everyone else should treat this as a demonstration—not a reason to buy expensive hardware for one match. The ordinary Apple TV broadcast remains the practical option for most viewers.
Apple security carry-forward: Macs still need attention from the August 6 security releases. Apple fixed CVE-2026-65400, a Screen Sharing authentication issue, in Tahoe 26.6.1, Sequoia 15.7.9, and Sonoma 14.8.9. Apple says a network attacker could authenticate without valid credentials; it does not say the flaw was exploited in the wild. Update the supported branch and disable unnecessary Screen Sharing until patched.
6. Boeing agrees to move Wisk, SkyGrid, and Insitu into Archer
Boeing agreed to transfer autonomous-aircraft developer Wisk Aero, airspace-software company SkyGrid, and drone maker Insitu to Archer in exchange for newly issued Archer shares, according to same-day reporting and an Archer regulatory filing. TechCrunch reports that the issuance equals 19.75% of Archer’s pre-closing outstanding shares and could leave Boeing with about a 16.5% stake after the transaction.
The strategic logic is broader than one aircraft. Wisk brings autonomous eVTOL work, SkyGrid contributes airspace software, and Insitu adds an established drone operation. Combined under Archer, those assets could strengthen technology, regulatory, defense, and operational capabilities. But “agreed” is not “closed,” and a transaction does not certify an aircraft, prove a commercial launch date, or eliminate integration risk.
Investors should read the filing’s closing conditions and dilution mechanics rather than trading on the headline alone. Aviation customers and partners should watch subsequent regulatory filings for completion, governance, and how the three businesses are integrated.
What did not happen today: no verified new Windows production update by cutoff
Microsoft’s official Windows 11 release information and Windows Message Center did not show a same-day production security, out-of-band, preview, or release-health update by the 5:12 PM EDT cutoff. Planned August hotpatch rows without an availability date, build number, or KB are plans—not releases.
That does not mean Windows administrators should relax. Keep normal update rings and backups ready, but do not invent an emergency based on an empty roadmap row. Use the quiet day to remove reused local-admin credentials with Windows LAPS and audit forgotten remote-support tools before they become someone else’s access path.
Your 20-minute action plan
- Edge appliances: search asset inventory for Progress LoadMaster and confirm the installed build against the vendor bulletin.
- Build infrastructure: identify every on-premises TeamCity server, restrict exposure, patch, and inspect logs before rotating secrets.
- Macs: deploy the appropriate August 6 security release and verify the running OS version—not just the MDM job result.
- Networks: if DNS complaints persist, compare multiple resolvers and regions before changing settings; rule out a local loop or provider issue.
- AI trials: put local agents in a sandbox with non-sensitive data, explicit permissions, logging, and spending/resource limits.
- Executive brief: tell decision-makers which items are active threats, which are resolved incidents, and which are future demonstrations. Those categories require different reactions.
Frequently asked questions
Does running MuseGlimmer locally make company data safe?
Not by itself. Local execution can reduce cloud exposure, but an agent may still access sensitive files, tools, network services, or third-party integrations. Use least privilege, a sandbox, logs, confirmation prompts, and a written data policy.
Was Cloudflare’s 1.1.1.1 service down worldwide?
No. Cloudflare described a minor degradation affecting multiple users in Tel Aviv and marked it resolved. The company did not publish evidence of a global outage.
Does CISA’s August 10 LoadMaster deadline apply to every business?
The deadline directly applies to covered federal agencies under CISA’s KEV process. Private organizations are not automatically bound by that date, but confirmed exploitation and unauthenticated command execution make immediate remediation prudent.
If TeamCity is patched, is the incident closed?
Not if the server was exposed while vulnerable. Patch first, then investigate accounts, tokens, service-process activity, configuration, stored-secret access, and build artifacts. Rotate credentials after containment.
Should I buy Vision Pro for one baseball game?
Probably not. Existing owners have a useful live demonstration to try. Everyone else should wait for independent reports on quality, latency, and comfort and remember that the standard Apple TV broadcast remains available.
Why include older security items in a daily recap?
Because an active exploitation update or a remediation deadline can be more operationally important than a same-day product announcement. Their older publication dates are labeled so readers are not misled.
Direct sources
- Meta AI Research — MuseGlimmer
- Cloudflare Status — Tel Aviv 1.1.1.1 incident
- CISA — Known Exploited Vulnerabilities catalog
- Progress — LoadMaster bulletin
- JetBrains — TeamCity active-exploitation guidance
- Apple Newsroom — Apple Immersive baseball announcement
- TechCrunch — Archer/Wisk transaction and Archer filing
- Microsoft — Windows 11 release information
- Apple security pages for Tahoe 26.6.1, Sequoia 15.7.9, and Sonoma 14.8.9
Reporting note: facts were checked against direct sources at the stated cutoff. Vendor benchmark and performance claims are identified as vendor-reported. Developing incidents and transactions can change after publication.