
Microsoft Agent Framework PyPI compromise: check for 1.26.1 and 1.26.2
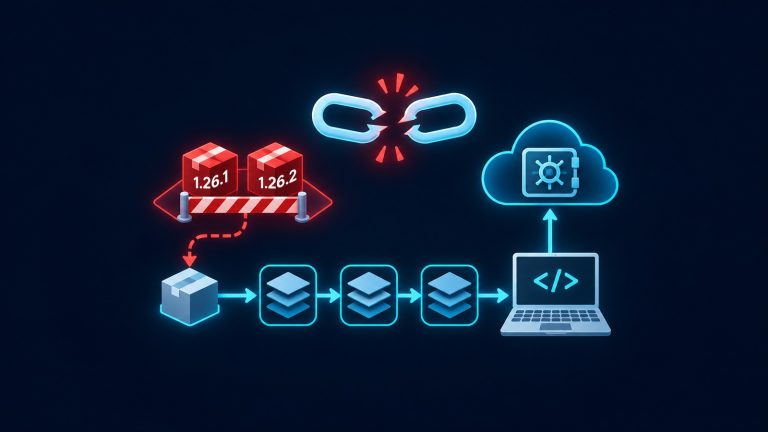
Microsoft Agent Framework PyPI versions 1.26.1 and 1.26.2 contained a credential stealer. Rebuild affected environments from a clean base and rotate reachable credentials.
Microsoft Agent Framework PyPI versions 1.26.1 and 1.26.2 contained a credential stealer. Rebuild affected environments from a clean base and rotate reachable credentials.
Apache says CVE-2026-129448 is a critical, actively exploited pre-authentication remote-code-execution flaw affecting Roller 4.0.0 through 6.1.5. Upgrade to 6.1.6 or later.
CVE-2026-129444 is a critical hard-coded-credentials flaw in the FTP daemon of D-Link DSL-6740C build 20131126. The model is end-of-life, and D-Link recommends discontinued use.
ENSAPIA Tokyo says unauthorized access to Hange servers exposed hashed-password, contact and payment-data records. In our complete multi-report page capture reviewed at the November 13 reporting cutoff, we found per-field counts but no unique-person total.
Red Hat Quay has a 9.8 unauthenticated signing-key takeover flaw and a 9.9 cross-tenant robot-token theft flaw. Fixed releases and practical response steps are available; no active exploitation was confirmed in the reviewed records at the reporting cutoff.
ConnectWise says its investigation is complete, but continued activity targets unpatched on-premises ScreenConnect systems with five extensions enabled. Verify every technician client is 26.6.5 or later; patching does not remove established persistence.
Microsoft says exploitation of Outlook CVE-2026-124194 has been detected. Practical guidance: update affected installations and verify the build.
CISA added two flaws to KEV on November 9, 2026. GPUStack names 2.2.0 as patched. IBM names Faspex 5.0.19 PL1.
Microsoft rates CVE-2026-109469 at CVSS 10.0 but says the Entra hosted service is fully mitigated and customers have no action to take.
SonicWall says CVE-2026-19868 can let a user with valid alternate-method credentials bypass SAML and SAML-enforced MFA on affected SSL-VPN systems. CISA lists it as known exploited. Here are the exact affected builds, fixed releases, exposure conditions, and verification steps.