
Loblaw Starts Notifying About Two Million People After March Data Breach
Loblaw is notifying about two million Canadians after its March breach. Here is what changed, why the payment-card wording needs care, and what affected people should do.
Loblaw is notifying about two million Canadians after its March breach. Here is what changed, why the payment-card wording needs care, and what affected people should do.
Twelve defensive case files: GitLab, LiteLLM, AI-monitoring failures, PHP2Shell, ClickFix, Bronze Sandcastle, Tor SSH interception, UpdraftCentral, DeepSeek, SBI, six CISA KEV additions, and Vasilek—separating confirmed exploitation, exposure, unknowns, and recovery.
Case File 040 maps a crowded security day: broken certificate trust, exploited access paths, poisoned developer tooling, an unresolved backup interruption, AI-assisted intrusion, spyware and privacy findings, and legal allegations kept inside their evidentiary bounds.
Hankyu Hanshin Department Stores says portions of about 1.26 million H2O ID records leaked. Here is what was confirmed, what remains under investigation, and what customers should do.
A calm, practical guide to spoofed bank calls: why caller ID proves nothing, the five rules that stop the scam, and what to do if you already shared money or account secrets.
Raven can rank candidate rentals and properties from interior photos—but its public demos are not an accuracy benchmark. Here’s what is verified, what remains unknown, and how to reduce your exposure.
Case File 039 separates active exploitation, in-the-wild malware, laboratory research, and legal allegations across twelve cybersecurity stories—and turns them into an evidence-first response plan.
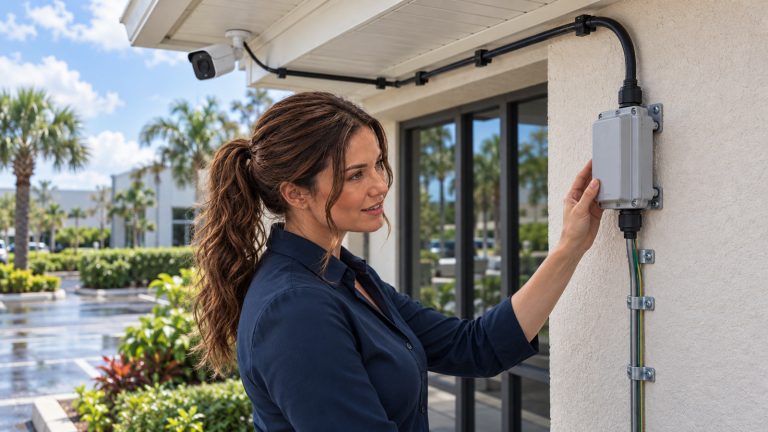
An outdoor PoE cable can carry a surge path toward your indoor switch, NVR, router, and firewall. Use this safe, model-aware audit before the next Florida storm.
Scammers can spoof real agency numbers, use real agents’ names, and stage official-looking video calls. Here is how to verify safely and what to do if you already paid.
Case File No. 036: MI5’s CGTRI research-security alert and a preserve-first defensive guide to Warlock ransomware activity targeting on-premises SharePoint.