
Microsoft Agent Framework PyPI compromise: check for 1.26.1 and 1.26.2
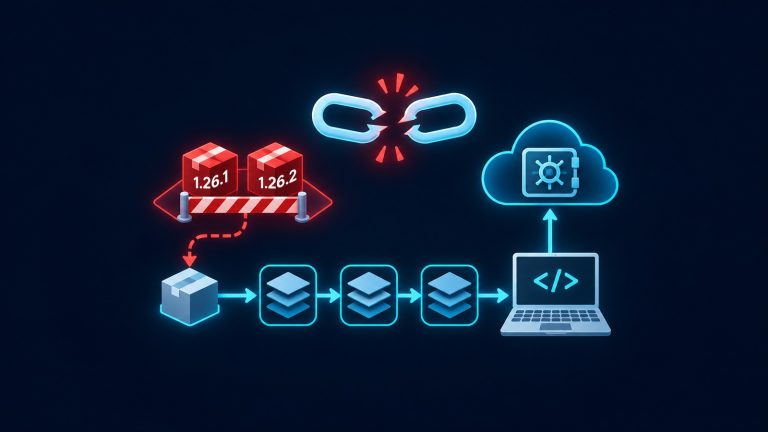
Microsoft Agent Framework PyPI versions 1.26.1 and 1.26.2 contained a credential stealer. Rebuild affected environments from a clean base and rotate reachable credentials.

Microsoft Agent Framework PyPI versions 1.26.1 and 1.26.2 contained a credential stealer. Rebuild affected environments from a clean base and rotate reachable credentials.
Apache says CVE-2026-129448 is a critical, actively exploited pre-authentication remote-code-execution flaw affecting Roller 4.0.0 through 6.1.5. Upgrade to 6.1.6 or later.
Five checked technology developments for November 17: Microsoft Ignite launches, new U.S. controls on remote access to advanced chips, OpenAI legal and allied-cyber programs, and free U.S. Apple TV coverage of the Las Vegas Grand Prix.
Access Dental Management says information may have been viewed and copied May 1–4. SecurityWeek reports 341,049 affected people across Texas and Vermont; the company notice gives no national total.
Five checked technology developments for November 16: GitHub bulk AI security scans, Google’s agentic-threat findings, AMD’s World Labs acquisition, new Google Cloud sovereignty controls, and IBM-NVIDIA-Fermilab quantum co-design plans.
Fandango says an unauthorized party could access card numbers, CVVs, expiration dates, billing ZIP codes and email addresses tied to certain October 8–11 checkout transactions.
Anthropic says a major Claude outage affecting claude.ai, the Claude API, Claude Code, and Claude Cowork was resolved after a 73-minute impact window.
Five checked technology developments for November 15: NVIDIA’s leadership uncertainty, Intel’s reported x86 share gain, Google’s school Search policy, GitHub Copilot model deadlines, and Singapore’s cyber-readiness warning.
CVE-2026-129444 is a critical hard-coded-credentials flaw in the FTP daemon of D-Link DSL-6740C build 20131126. The model is end-of-life, and D-Link recommends discontinued use.
Coinone says an attacker breached outsourced support provider MetaM and exposed customer-submitted support data; affected fields vary and no count is disclosed.