
Microsoft Agent Framework PyPI compromise: check for 1.26.1 and 1.26.2
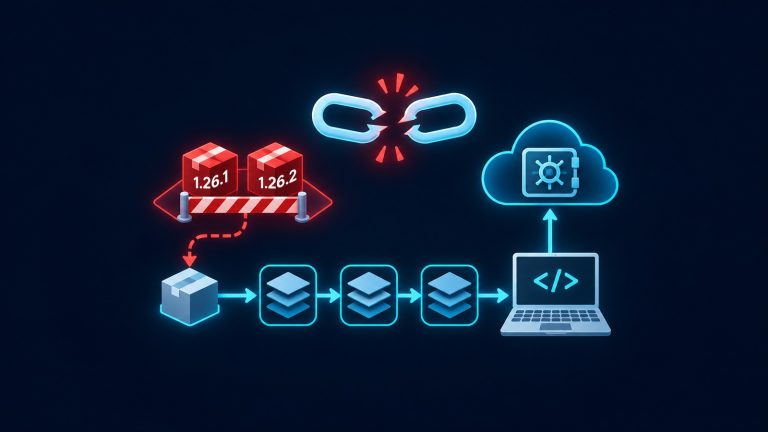
Microsoft Agent Framework PyPI versions 1.26.1 and 1.26.2 contained a credential stealer. Rebuild affected environments from a clean base and rotate reachable credentials.
Microsoft Agent Framework PyPI versions 1.26.1 and 1.26.2 contained a credential stealer. Rebuild affected environments from a clean base and rotate reachable credentials.
Apache says CVE-2026-129448 is a critical, actively exploited pre-authentication remote-code-execution flaw affecting Roller 4.0.0 through 6.1.5. Upgrade to 6.1.6 or later.
CVE-2026-129444 is a critical hard-coded-credentials flaw in the FTP daemon of D-Link DSL-6740C build 20131126. The model is end-of-life, and D-Link recommends discontinued use.
ENSAPIA Tokyo says unauthorized access to Hange servers exposed hashed-password, contact and payment-data records. In our complete multi-report page capture reviewed at the November 13 reporting cutoff, we found per-field counts but no unique-person total.
Red Hat Quay has a 9.8 unauthenticated signing-key takeover flaw and a 9.9 cross-tenant robot-token theft flaw. Fixed releases and practical response steps are available; no active exploitation was confirmed in the reviewed records at the reporting cutoff.
Microsoft says exploitation of Outlook CVE-2026-124194 has been detected. Practical guidance: update affected installations and verify the build.
SonicWall says CVE-2026-19868 can let a user with valid alternate-method credentials bypass SAML and SAML-enforced MFA on affected SSL-VPN systems. CISA lists it as known exploited. Here are the exact affected builds, fixed releases, exposure conditions, and verification steps.
NTT DOCOMO says unauthorized access to Online Shop and My docomo leaked some customer information, with a stated maximum of about 300,000 records.
OpenSSH and Alpine Linux have fixed a critical SSH password-authentication bypass that requires musl libc, PAM-disabled authentication, password logins, and specific account states.
Ryohin Keikaku and Credit Saison say full MUJI Card numbers may have been accessed in a roughly 1.09 million-record cohort. Here is what customers should check now.