

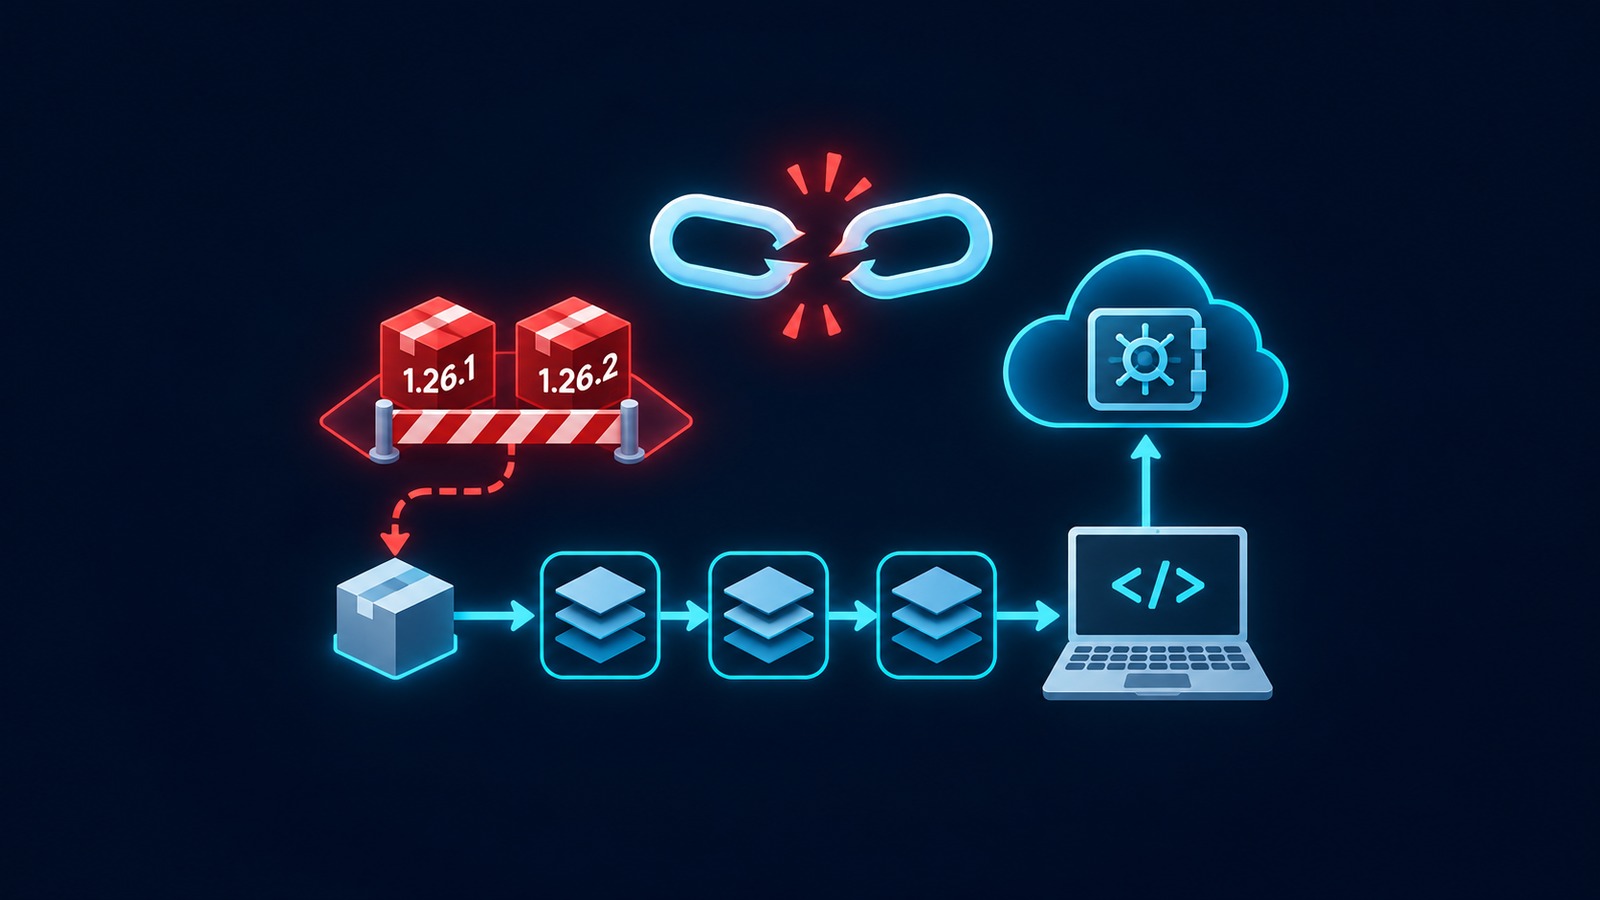
Two releases of the legitimate Microsoft agent-framework package on PyPI—1.26.1 and 1.26.2—contained a credential stealer.3 PyPI quarantined both releases and points users to 1.26.0 instead.12
CREDENTIAL STEALER • Reporting cutoff: November 18, 2026 at 12:52:17 AM EST (05:52:17 UTC).
The bottom line
If either affected version was installed, treat that environment and the credentials it could read or request as exposed.3 Isolate it before starting Python or pip, rebuild from a clean base, and treat credentials the payload could read or request as potentially exposed.4
Verified facts
What happened
StepSecurity reports 1.26.1 as uploaded at 20:35:20 UTC and quarantined at 21:06:16 UTC on November 17, 2026.4 The report records 1.26.2 as uploaded at 21:08:39 UTC and quarantined at 21:16:44 UTC.4 The second upload landed 2 minutes 23 seconds after the first quarantine; that shows publishing access still worked at that moment, not that it remains available now.4
| Version | Uploaded UTC | Quarantined UTC | Wheel SHA-256 |
|---|---|---|---|
| 1.26.11 | 2026-11-17 20:35:201 | 2026-11-17 21:06:161 | d27fa34414e6201d5e03e559ef634f020057554d7b3f4898dd5d7cd3e989e1101 |
| 1.26.22 | 2026-11-17 21:08:392 | 2026-11-17 21:16:442 | 3d20a8bc91351a9a16b6db243b848ceca0206b7a8623b02d2af553a9c9f7e0a92 |
Why Python startup matters
Both wheels added executable .pth startup hooks, which Python processes during site initialization; the stealer could run on a later Python startup without an explicit import agent_framework.3 In 1.26.1, the path was agent_framework_meta.pth with agent_framework_meta/_telemetry.py.3 In 1.26.2, it moved to af_runtime_diag.pth and af_runtime_diag.py, while the package initializer matched clean 1.26.0; checks limited to the first layout can therefore miss the second.35
The collector targeted host context, secret-like environment variables, readable process environments, and named credential files; 1.26.2 also added GitHub Actions OIDC token requests and runner paths.3 It compressed and encoded collected data before an HTTPS POST to a fixed webhook.site path.3 StepSecurity’s static review found no remote-code-loading second stage in the inspected payloads.4
Static analysis describes collection and transfer attempts; it does not by itself prove completed exfiltration.34 Investigate requests to the exact incident path and distinguish blocked attempts from successful transfers; a domain connection alone does not confirm exfiltration.4
Scope: the meta-package, not every sibling
Endor Labs reported that the thin agent-framework meta-package was modified, while the 22 sibling agent-framework-* packages it checked—including agent-framework-core—had no newer release than November 12.5 That is a bounded reviewed set, not proof that every related package, private mirror, or internal artifact is clean.45
What this means for a small business
Practical guidance: any environment that installed agent-framework 1.26.1 or 1.26.2 is in scope for containment and review.34 PyPI quarantine blocks normal installation or modification pending review; environments that already installed an affected version still require isolation and a clean rebuild.124
- Contain before normal Python work.34 If an affected version is present, isolate the affected environment before starting Python or
pip, because another interpreter start can process the hook again.34 - Audit egress logs.4 Audit egress logs for requests to the exact incident path and distinguish blocked attempts from successful transfers.4
- Rebuild rather than only deleting the hook.4 Rebuild affected environments from a clean base, then pin a trusted dependency set to
agent-framework==1.26.0.4 Removing one.pthfile does not prove that a detached collector stopped.4 - Pin the clean version and rebuild.4 Pin dependency policy to
agent-framework==1.26.0and rebuild affected environments from a clean base.4 - Rotate from a clean system.34 Rotate credentials the environment could read or request, including applicable CI and GitHub Actions secrets.34
- Hunt both layouts and both hashes.34 Hunt for
agent_framework_meta.pth,af_runtime_diag.pth, and the two wheel hashes in the table.34 - Investigate transfer outcomes.4 Investigate outbound requests to the exact incident path and distinguish blocked attempts from successful transfers.4
- Verify recovery.34 Confirm the rebuilt environment contains neither affected version, neither
agent_framework_meta.pthnoraf_runtime_diag.pth, and uses the intended clean dependency set.34
Microsoft’s acknowledgment and the evidence limit
A Microsoft repository member said the two compromised versions had been pulled and that Microsoft was investigating.6 At the independent check, Microsoft Agent Framework issue #10411 returned GitHub 404 in direct browser and API requests.6 The quoted acknowledgment is preserved from a current search-index snapshot for the primary issue URL rather than a directly readable issue body.6 At the reporting cutoff, the package had captured an indexed Microsoft acknowledgment and direct 404 results, not a directly readable Microsoft root-cause or customer-impact report.6
What remains unknown
- The initial access vector, uploader identity, and specific compromised account or credential remain unconfirmed.4
- StepSecurity advises checking the exact path and transfer outcome; a domain connection alone does not confirm exfiltration.34
- At the reporting cutoff, the package had not captured a directly readable Microsoft root-cause or customer-impact report.6
- The evidence does not support a blanket claim that every related package or private mirror is clean.45
Sources
- PyPI — agent-framework 1.26.1 quarantine record — accessed November 18, 2026.
- PyPI — agent-framework 1.26.2 quarantine record — accessed November 18, 2026.
- OpenSSF/OSV — MAL-2026-20101 — accessed November 18, 2026.
- StepSecurity — Microsoft agent-framework PyPI Package Compromised — published November 18, 2026.
- Endor Labs — agent-framework compromised — accessed November 18, 2026.
- Microsoft Agent Framework issue #10411 — direct page unavailable at the reporting cutoff; acknowledgment preserved from a search-index snapshot.
Update and correction note: This article is bounded to the cited sources and the reporting cutoff. Quarantine status can change.12 Response decisions should be based on the installed version and preserved local evidence—not on registry availability alone.34