Reporting cutoff: October 19, 2026, 11:50 a.m. Eastern (15:50 UTC). This is a point-in-time account of an active investigation; victim and provider findings may change.
A human operator, not an AI acting on its own, set the targets and goals. What changed was the amount of work the operator could delegate. NorForge says it watched a Chinese-speaking operator use exposed instances of the open-source Cairn framework; Reuters reported that the operator’s agents attempted more than 1,200 websites and independently reviewed the Cairn activity to identify victims associated with more than 100 apparent compromises, including limited web properties associated with Deere & Company and SharkNinja and a potential incident involving a Cummins vendor-operated site. Neither source established that the operator was in China or acting for a state. [1] [2]
What happened
NorForge researcher Snorre Fagerland reported finding roughly two dozen exposed Cairn instances used for apparently malicious activity beginning around October 2. NorForge grouped 14 panels into its most active cluster, labeled AIA0001, based on shared hosting, language, task patterns and other operational links. The firm said those panels contained more than 1,100 projects; Reuters reported that the operator’s agents had attempted more than 1,200 sites by late the week of October 12. The difference is a reminder that these are changing snapshots, not a final census. [1] [2]
NorForge’s captured examples show an operator supplying a target set, desired outcome and priorities; Cairn then assigned work to agents, collected findings and pursued paths toward the defined goal. Reuters described instructions shorter than 100 Chinese characters in some cases. Chinese-language use is evidence about the working language, not reliable proof of nationality, location or government sponsorship. [1] [2]
NorForge said it validated some claimed compromises by checking whether the reported result existed, and Reuters said it independently reviewed the operator’s Cairn activity to establish victim identities. Reuters could not determine how often unauthorized access led to extraction of data. Editorial distinction: this article therefore keeps access, persistence and data theft as separate outcomes. [1] [2]
Victim-by-victim status
| Organization | What the company told Reuters | Boundary on the claim |
|---|---|---|
| Deere & Company (John Deere) | Deere said it took “necessary remediation actions” and had “no indication that sensitive information was accessed.” [2] | This statement does not establish an intrusion into tractors, machinery, operational technology, customer accounts or Deere’s wider enterprise network. |
| SharkNinja | SharkNinja said a standalone product-support website was affected and the threat was contained. [2] | The statement is about a standalone support site, not SharkNinja appliances, customer devices or the whole corporate environment. |
| Cummins | Cummins said it was investigating a report of a potential cyberattack on a website operated by a third-party vendor. [2] | “Potential” and “investigating” matter: this was not a company confirmation of a completed compromise, and the referenced site was vendor-operated. |
Reuters also reported that two smaller businesses acknowledged compromises, while other organizations did not respond. We are not naming additional victims from exposed attacker data. [2]
How Cairn works — at a safe, high level
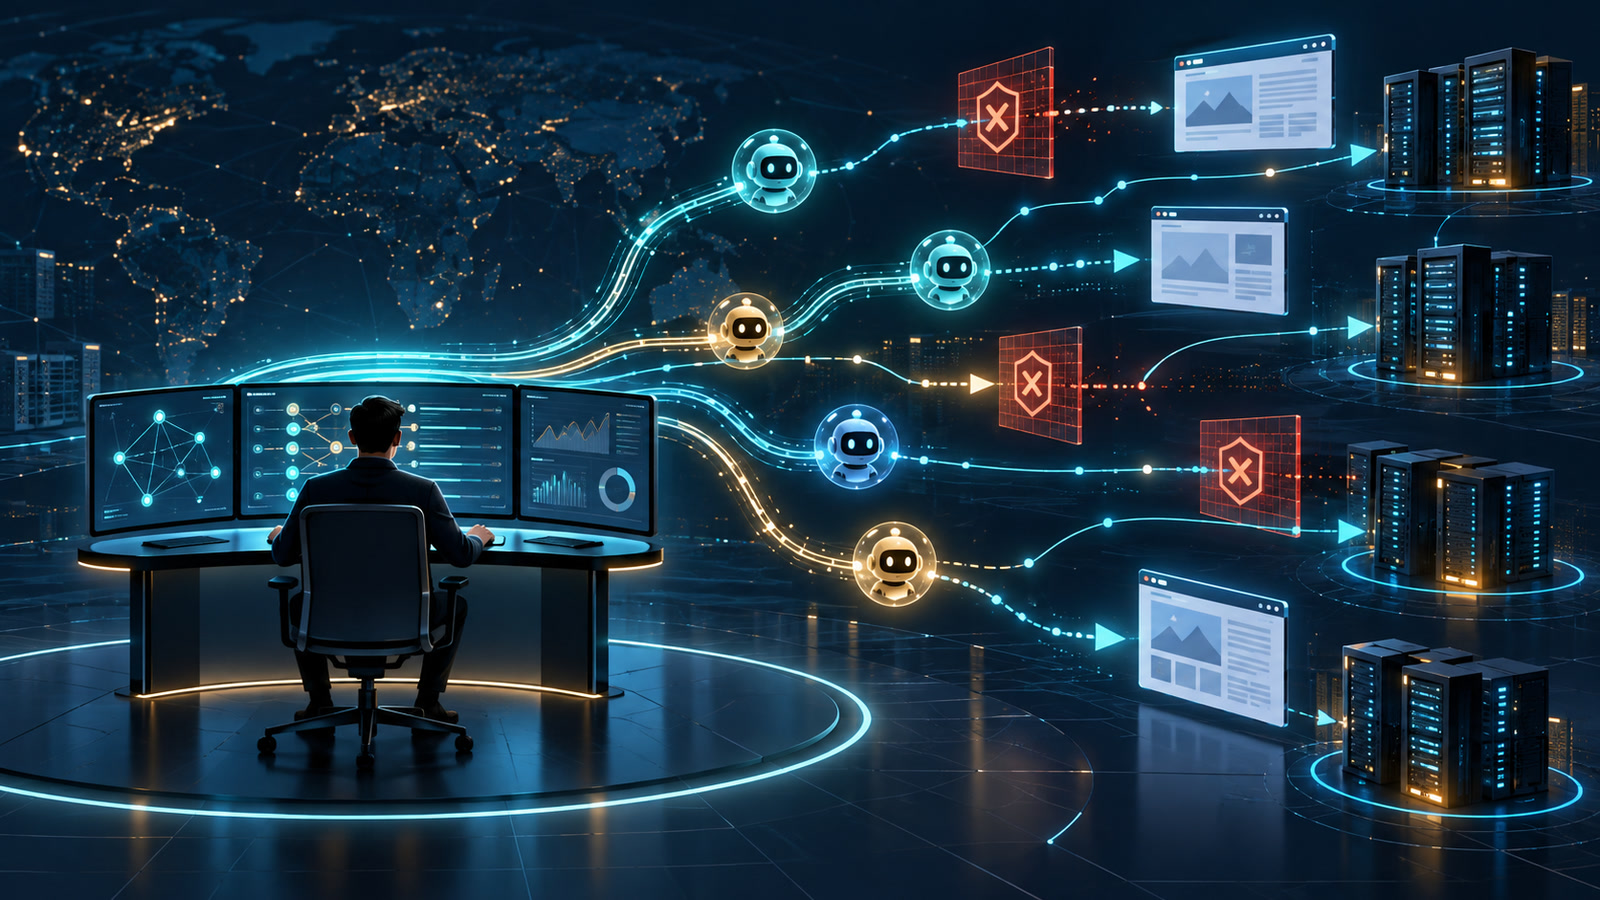
Editorial classification: Cairn’s own documentation describes a general-purpose state-space search engine; this article does not classify the framework itself as malware. A project begins with an origin and a human-defined goal. A shared blackboard holds confirmed “facts,” proposed “intents” and human “hints.” A dispatcher schedules tasks and worker containers; agents read the shared graph, explore one path, and write structured findings back. Supported worker back ends include Claude Code, Codex and Pi. [3]
That architecture can support authorized research, vulnerability testing and capture-the-flag work. The repository’s disclaimer requires explicit authorization and disavows harmful use. The same flexible orchestration can be misused when an operator points it at systems without permission. Editorial classification: calling Cairn “malware” would therefore be misleading: the reported offense lies in the operator’s goals and unauthorized use, while any payloads or persistence tools are separate components. [1] [3]
NorForge’s observation adds a practical detail: workers can pursue many possible paths, share discoveries through the blackboard and continue with limited supervision. “Limited supervision” is more accurate than “no human involvement,” because a person selected targets, wrote goals, supplied hints and operated the infrastructure. [1]
Scale, speed and cost — with denominators attached
NorForge separately estimated an average success rate near 10% across the harnesses it observed, while warning that clusters differed and “success” did not mean the same thing in every task. That rough estimate should not be treated as a universal AI-hacking benchmark. NorForge also estimated about $5 per project when unsuccessful and short runs were included, with some long projects potentially exceeding $100; Reuters’ roughly $50-per-success figure uses a different denominator. [1] [2]
Do not merge this campaign with Gambit Security’s September case. Reuters described an earlier, different Gambit investigation involving attacks on 25 companies and at least 600,000 payment-card records. Those companies and records are not part of the Cairn operator’s 100-plus count. [2]
Chronology
- September 25: Reuters says the prolific operator began directing agents against e-commerce sites in the United States, Canada, Australia and Japan. [2]
- Around October 2: Fagerland told Reuters that he began finding exposed Cairn instances associated with malicious activity. [2]
- Following weeks: NorForge observed projects, grouped related panels, validated selected outcomes and worked with Reuters on victim notification. [1]
- October 19: NorForge published its technical investigation and Reuters published its independent report and company responses. [1] [2]
Why exposed agent control planes matter
NorForge’s window came from dashboards left open on the public internet. The firm said those panels exposed target details, agent findings, human input and, in some cases, secrets. It reported scanning captured material with TruffleHog and finding hundreds of secret-like values, 11% of which the tool verified as valid. Those are NorForge’s observations about the exposed operation, not proof that every value came from a victim or that each one was used. [1]
[1][3] Practical risk-based guidance: treat any agent platform that can call tools, retain context and act on external systems as an administrative control plane. Apply authentication, isolation, least privilege, logging and documented exposure decisions—the same protective outcomes NIST CSF 2.0 organizes under Govern, Protect and Detect. [5]
Practical defensive actions
For website owners and small businesses
- Inventory internet-facing sites, including support portals and vendor-operated properties. NIST CSF 2.0 places asset and risk understanding under Identify and supply-chain governance under Govern. [5]
- Require phishing-resistant MFA for administrative access where available, remove default credentials, and limit remote administration. CISA’s archived cross-sector goals prioritize MFA and protections for externally accessible assets; organizations should also check CISA’s current CPG materials for updates. [6]
- Risk-based application: patch exposed applications and retire unsupported components; when compromise is suspected, preserve evidence before destructive cleanup. NIST CSF 2.0 includes incident analysis and evidence-integrity outcomes, while CISA’s archived goals call for access- and security-focused logging for detection and response. [5] [6]
- Use tested backups stored separately from source systems and maintain an incident-response plan. CISA’s archived goals recommend separate, recurringly tested backups and maintained, exercised response plans. [6]
- Risk-based vendor-responsibility prescription: make third-party website ownership explicit. Contracts should identify who patches, monitors, preserves logs, receives security reports and can take a site offline. NIST CSF 2.0 includes cybersecurity supply-chain risk management in Govern. [5]
For agent and security-tool operators
- Risk-based application of NIST Protect and Detect: do not expose orchestration dashboards to the internet by default; place them behind strong authentication, network restrictions and monitored administrative access. [5]
- Risk-based application of least privilege: separate projects and secrets; give workers only the credentials and network reach required for an explicitly authorized engagement. [5]
- Risk-based logging recommendation: log human instructions, tool calls, worker outputs and configuration changes, and alert on disabled logging or unexpected target changes. NIST supports continuous monitoring; CISA’s archived goals call for security-focused logs and notification when a critical log source is disabled. [5] [6]
- Editorial safety recommendation: use enforceable target allowlists and stop conditions rather than relying on a natural-language disclaimer alone. This is a design recommendation derived from the exposed-panel risk, not a measured guarantee. [1]
Frequently asked questions
Were John Deere tractors or farm machinery hacked?
There is no evidence in the reviewed reporting that tractors, farm machinery or operational technology were compromised. Deere’s statement concerned remediation after an incident and said it had no indication sensitive information was accessed. [2]
Was customer data stolen?
Unknown. Reuters could not determine the extent of unauthorized data extraction. Deere said it had no indication sensitive information was accessed; SharkNinja described a contained incident on a standalone product-support site; Cummins was still investigating a potential attack on a vendor-operated site. [2]
Did AI choose the victims and attack on its own?
No. A human operator selected targets and goals. Agents performed much of the reconnaissance and intrusion work with limited supervision, using shared findings to pursue paths toward the operator-defined outcome. [1] [2]
Is Cairn malware?
Editorial classification: Not by itself. Cairn is an open-source general problem-solving and orchestration framework whose documentation includes authorized penetration testing and research uses. It can be misused when a person directs it against systems without permission. [3]
Did the operator really spend only $50 per successful compromise?
That is a researcher estimate reported by Reuters, not a verified invoice. Fagerland estimated about $5,000 in token costs for the campaign and roughly $50 per successful intrusion. [2] Model pricing, caching, failed attempts and the definition of success make the number uncertain. [1]
What should I do if I operate a website?
Risk-based checklist: confirm every public-facing asset and vendor owner, restrict administrative access, use strong MFA, patch exposed software, preserve and centralize logs, test backups, and rehearse a response plan. If indicators suggest active compromise, follow that plan and preserve incident evidence before destructive cleanup. NIST CSF 2.0 supports incident analysis and evidence integrity; CISA’s archived cross-sector goals support MFA, logging, backups and response planning. [5] [6]
Sources
- NorForge, “Inside Cairn: Open Windows into massive AI-Driven Cyber Operations,” October 19, 2026 — researcher observations, cluster methodology, architecture description, estimated success/speed/cost, exposed-panel findings and case validation.
- Reuters via Insurance Journal, Raphael Satter, “How One Hacker Used AI Agents, a Few Thousand Dollars to Break Into Websites,” October 19, 2026 — Reuters’ independent review, victim identification, company statements, scale and cost reporting.
- Cairn official GitHub repository — project purpose, origin/goal model, blackboard architecture, dispatcher/workers, supported back ends and authorization disclaimer.
- Gambit Security, separate September 2026 investigation — background reading linked from Reuters; the figures used above are attributed to Reuters because the preserved Gambit snapshot did not contain the report body.
- NIST Cybersecurity Framework 2.0 — Govern, Identify, Protect, Detect, Respond and Recover outcomes.
- CISA Cross-Sector Cybersecurity Performance Goals (archived page) — dated baseline guidance on MFA, logging, backups, exposed-asset protection and incident-response planning; readers should check CISA’s current CPG materials for updates.
- CERT-In Cyber Security Directions of April 28, 2022 — scope, six-hour incident reporting and 180-day log retention.
Editorial image: AI-generated illustration showing a generic human-directed agent workflow; it does not depict a real operator, victim, interface or infrastructure.