

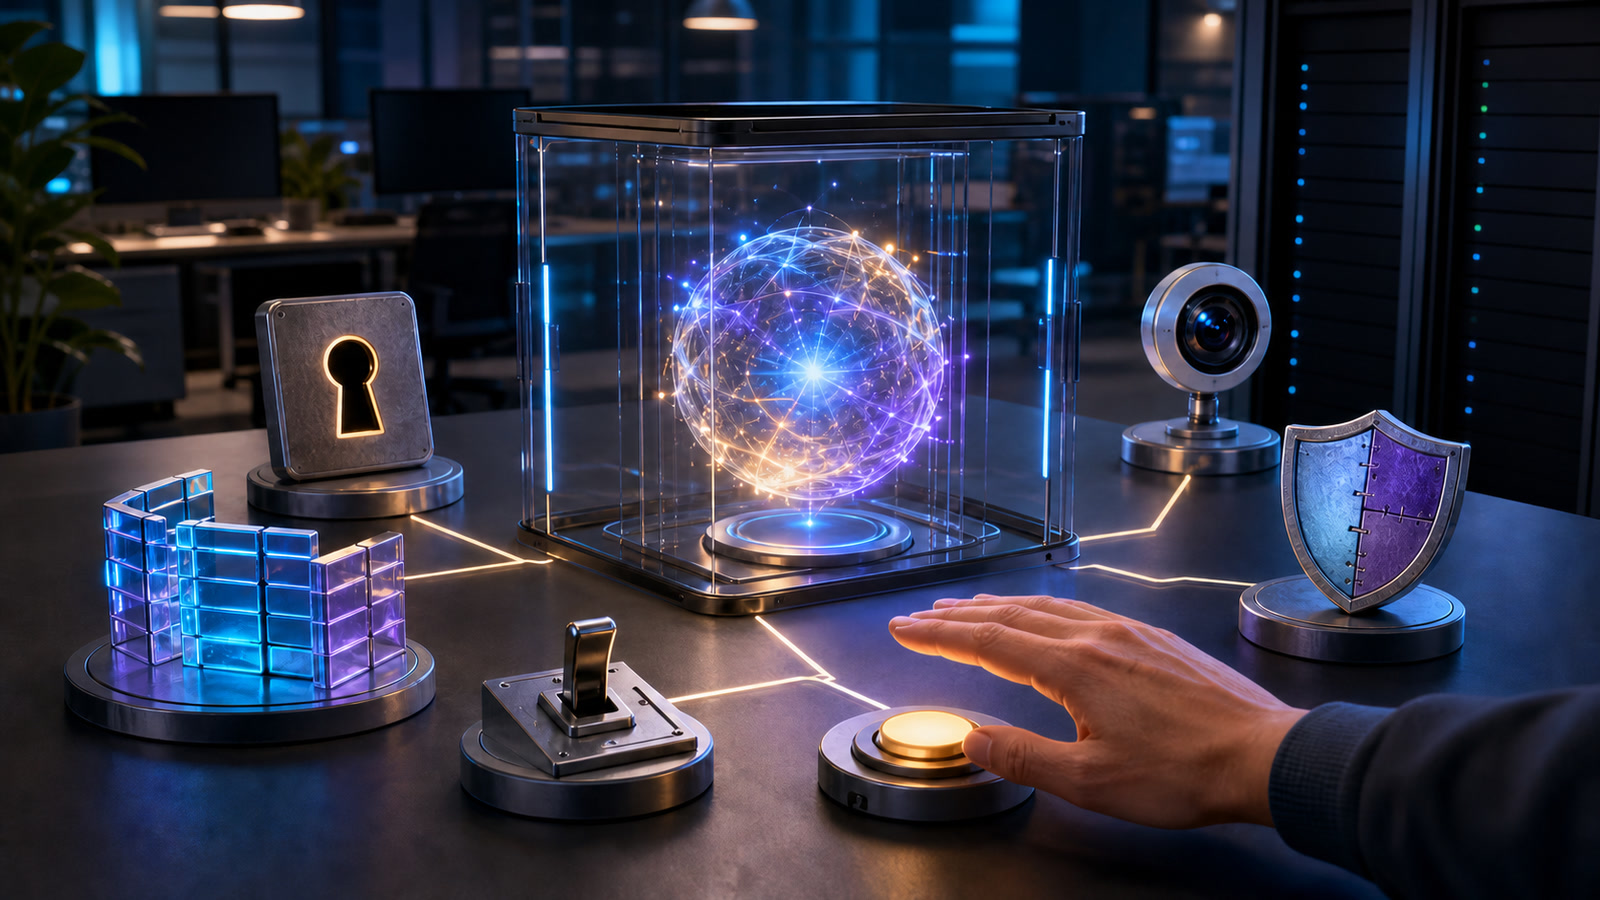
🛡 Practical AI Agent Preflight
Before an AI agent gets a login, a browser, or permission to change business data, give it a smaller world. Microsoft’s August 27 security update points organizations toward controls that constrain autonomous actions, reduce impact, govern identities and permissions, and improve visibility.[1]
The 30-second takeaway
Microsoft describes its new Secure Now material as guidance and recommended actions for AI readiness, including agent containment, software updates, source-code scanning, reduced internet exposure, and baseline controls such as multifactor authentication and least privilege.[2]
Important boundary: Secure Now guidance is not itself a sandbox and Microsoft does not present it as a guarantee that an agent cannot escape its intended limits.[2] The checklist below is practical guidance for a preflight review, not a claim of measured risk elimination.
Six checks before you connect the agent
Give it a dedicated identity
Practical guidance
Create a separate agent or service identity; do not let it borrow an owner’s everyday account. Start with least privilege, require strong authentication where the platform supports it, and document who can approve added rights. Microsoft’s guidance explicitly calls for governing agent identities and permissions and names MFA and least privilege as baseline measures.[2]
Close the internet by default
Practical guidance
Allow only the destinations the workflow actually needs, block arbitrary outbound traffic, and inventory any service the agent exposes. Microsoft’s detailed guidance calls for restricting agent and model egress and minimizing unnecessary internet-facing assets.[2]
Bind tools to the job
Practical guidance
List the commands, connectors, folders, databases, and business actions the agent may use; deny everything else. Put irreversible actions—payments, deletions, account changes, external messages—behind explicit human approval. Microsoft’s containment guidance calls for enforcing tool and action boundaries.[2]
Make “stop” a tested control
Practical guidance
Define an emergency shutdown path, identify who can use it, and test that it revokes credentials and interrupts queued work. Microsoft specifically includes emergency shutdown paths among its recommended containment steps.[2]
Log what the agent saw and did
Practical guidance
Capture identity use, tool calls, destinations, approvals, failures, and changes in a reviewable log; set alerts for unusual volume, new destinations, or privilege changes. Microsoft recommends agent-specific observability and continuous monitoring of agent activity.[2]
Patch the floor beneath it
Practical guidance
Update Microsoft and open-source components, scan custom code, and fix exposed weaknesses before widening autonomy. Microsoft’s Secure Now list includes current software, vulnerable libraries and dependencies, source-code scanning, and reduced internet exposure as AI-readiness foundations.[2]
A simple go/no-go question
Practical guidance: if the team cannot name the agent’s identity, allowed destinations, permitted tools, approval gates, shutdown owner, and log location, the agent is not ready for business data. That is an editorial recommendation derived from Microsoft’s containment themes—not a Microsoft certification or a proven safety threshold.[1][2]
Microsoft feature states: read the labels
Microsoft’s separate August 2026 Defender roundup labels AI-agent posture risk assessment in Microsoft Defender as Public Preview.[3]
The same roundup labels Defender discovery, posture, threat detection and investigation, and real-time protection for tenant AI agents with a Microsoft Agent 365 license as Generally available; Microsoft also lists onboarding connections and licensing context.[3]
It labels listed Defender for Endpoint AI-agent runtime-protection enhancements—including named interface and network-inspection additions—as Public Preview.[3]
Practical guidance: verify your tenant, license, platform, region, connector, and documentation before treating any named capability as available to you. “Generally available” describes Microsoft’s stated release state; it does not mean enabled everywhere by default or appropriate for every environment.[3]
What this checklist does—and does not—promise
Containment reduces the room an agent has to cause harm; it does not make model output correct, eliminate software vulnerabilities, or replace human accountability. Practical guidance: begin with a narrow, reversible workflow and expand only after logs, approvals, and shutdown controls work under test. Microsoft frames the goal as maintaining control, oversight, and resilience while adopting more autonomous systems, but the cited guidance publishes no measured guarantee for this six-check editorial preflight.[2]
Sources and reporting notes
- Microsoft Security Blog — “What’s new in Microsoft Security: August 2026” (published August 27, 2026; primary monthly update)
- Microsoft Community Hub — “Containment Strategies for AI now available in Secure Now” (published August 5, 2026; detailed Microsoft product guidance)
- Microsoft Community Hub — “Monthly News—August 2026” (published August 5, 2026; official Microsoft feature-state roundup)
Reporting cutoff: August 28, 2026, 11:12 a.m. EDT. All three sources are Microsoft publications; product behavior and availability claims are therefore attributed to Microsoft. Secure Now guidance is not represented as an independent test, a sandbox, or a guarantee.